PMA Lab 6-3: C Code Constructs in Assembly
In this lab, we’ll analyze the Malware found in the file Lab06-03.exe.
Lab 6-3
In this lab, we’ll analyze the Malware found in the file Lab06-03.exe.
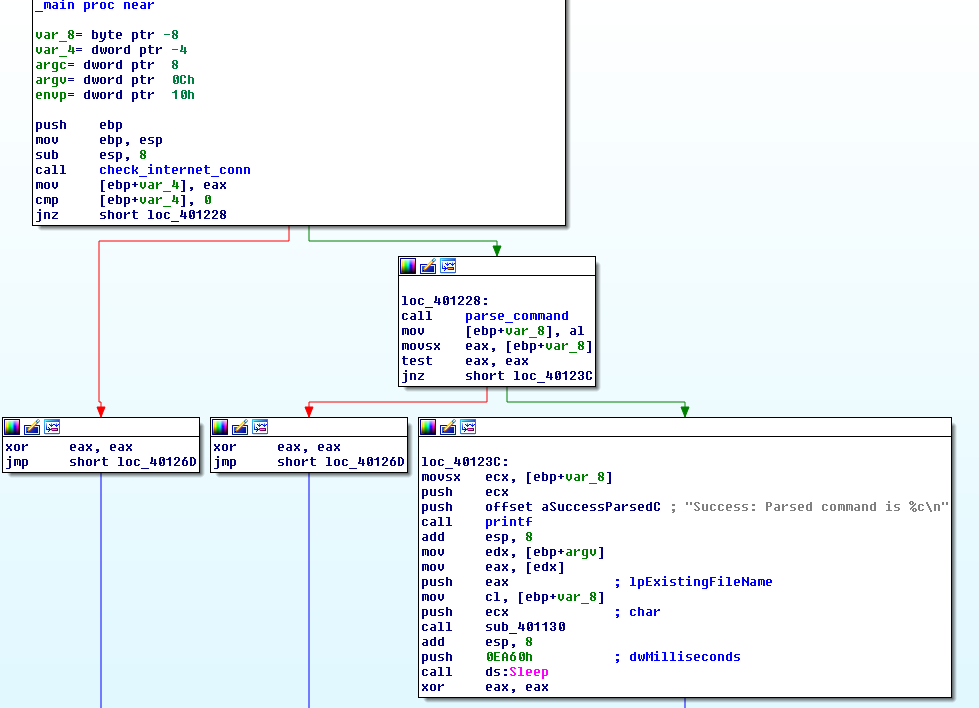
1) Compare the calls in main to Lab 6-2’s main method. What is the new function called from main ?
After taking a look at main we see the previously observed check_internet_conn, parse_command and, printf subroutines. The new subroutine is sub_401130 at 0x00401258
2) What parameters does this new function take?
This function takes two parameters:
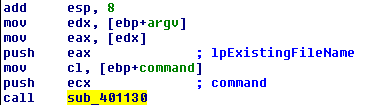
The first argument is the command returned from parse_command and the second one is argv (ebp+argv - parameter provided to the program) and has been automatically commented as lpExistingFileName.
3) What major code construct does this function contain?
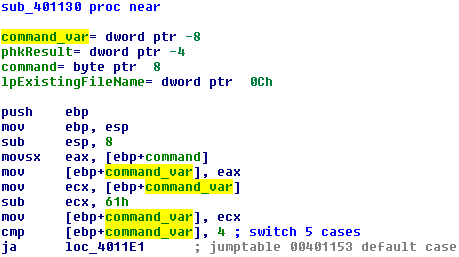
This function contains a switch statement with a jump table to make a decision based on the returned command by parse_command (sub_401040):
4) What can this function do?
Taking a look at the Switch case and respective branch functions, this Malware can take commands to:
- Create a Directory C:\Temp
- Copy the file provided as a parameter to C:\Temp\cc.exe
- Delete C:\Temp\cc.exe
- Create persistency for C:\Temp\cc.exe
- Key: HKLM\Software\Microsoft\Windows\CurrentVersion\Run
- Name: Malware
- Value: C:\Temp\cc.exe
- The Malware can sleep for 100 seconds.
5) Are there any host-based indicators for this Malware?
The Registry key and directory/filename provided in 4) can be used as host-based indicators for this Malware.
6) What is the purpose of this Malware?
The Malware checks whether or not it has an active connection to the Internet, then retrieves a command from a Web page (hidden in a commentary) and execute. There are 5 different commands as seen in 4):
- Create a Directoy
- Copy a provided file to C:\Temp\cc.exe
- Delete C:\Temp\cc.exe
- Create persistency for said file
- Sleep for 100 seconds