PMA Lab 3-1: Basic Dynamic Analysis
1) What are this malware’s imports and strings?
Lab 3-1
1) What are this malware’s imports and strings?
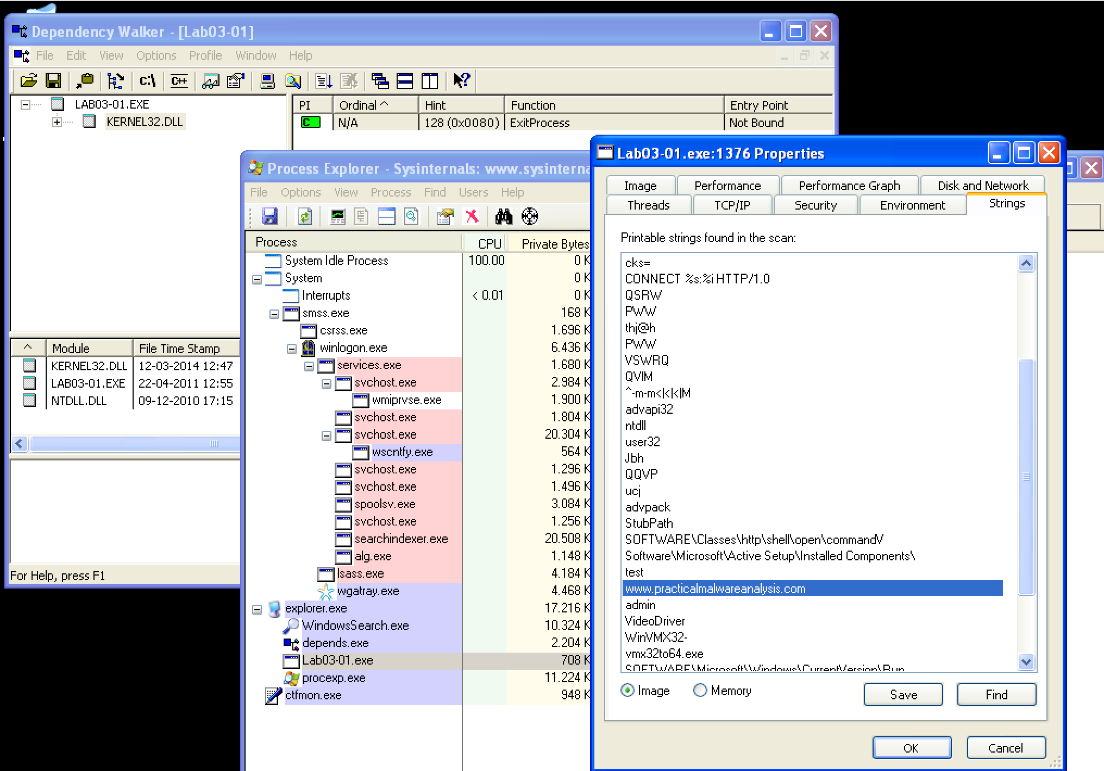
The Malware appears to be packed since it only has one Import: ExitProcess.
However, as we can see with Process Explorer, there is a reasonable amount of readable strings.
2) What are the malware’s host-based indicators?
As soon as we run the file, Process Monitor is flooded with events, most of them not being useful.
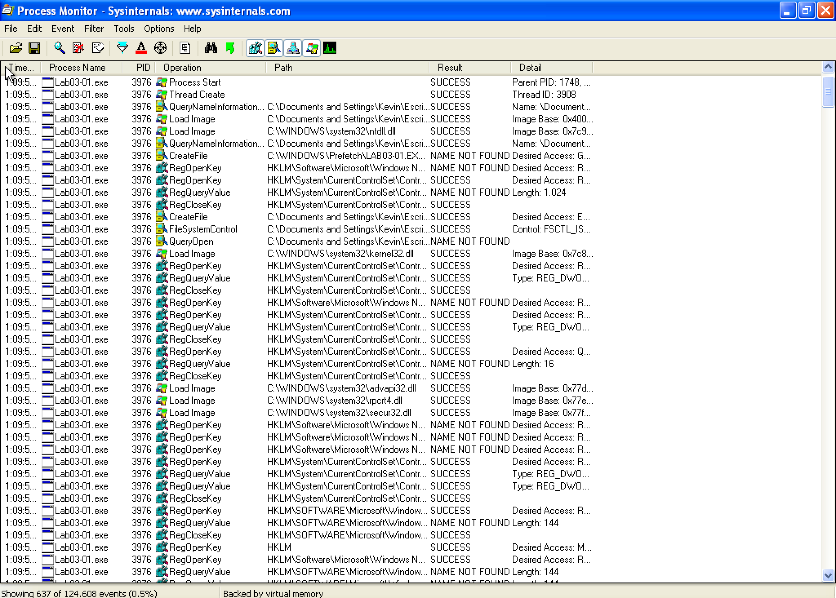
In this case, it is a good idea to filter the events. Filtering by Operation, with the values WriteFile and RegSetValue we can see that the following changes were made in the file system and register.
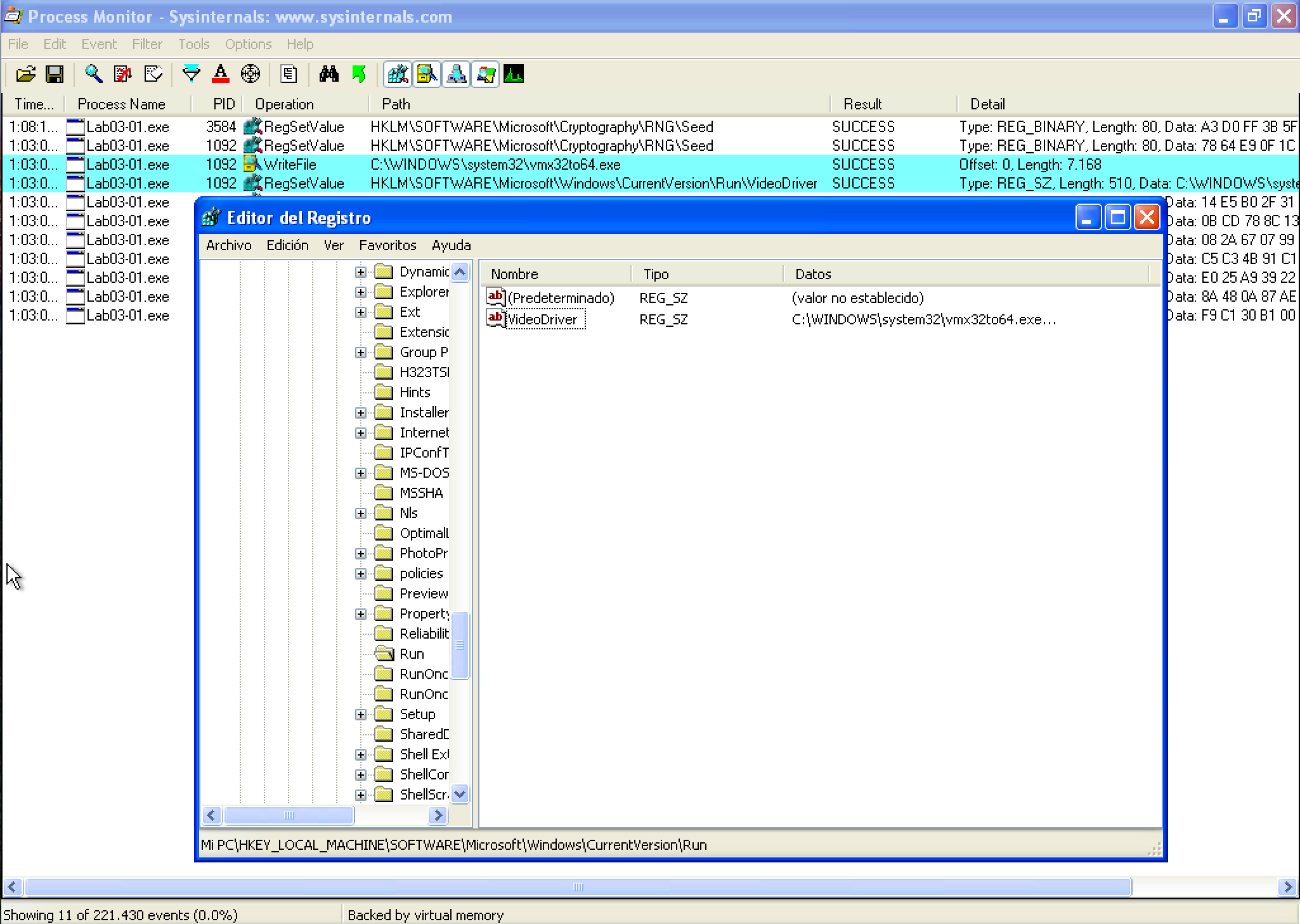
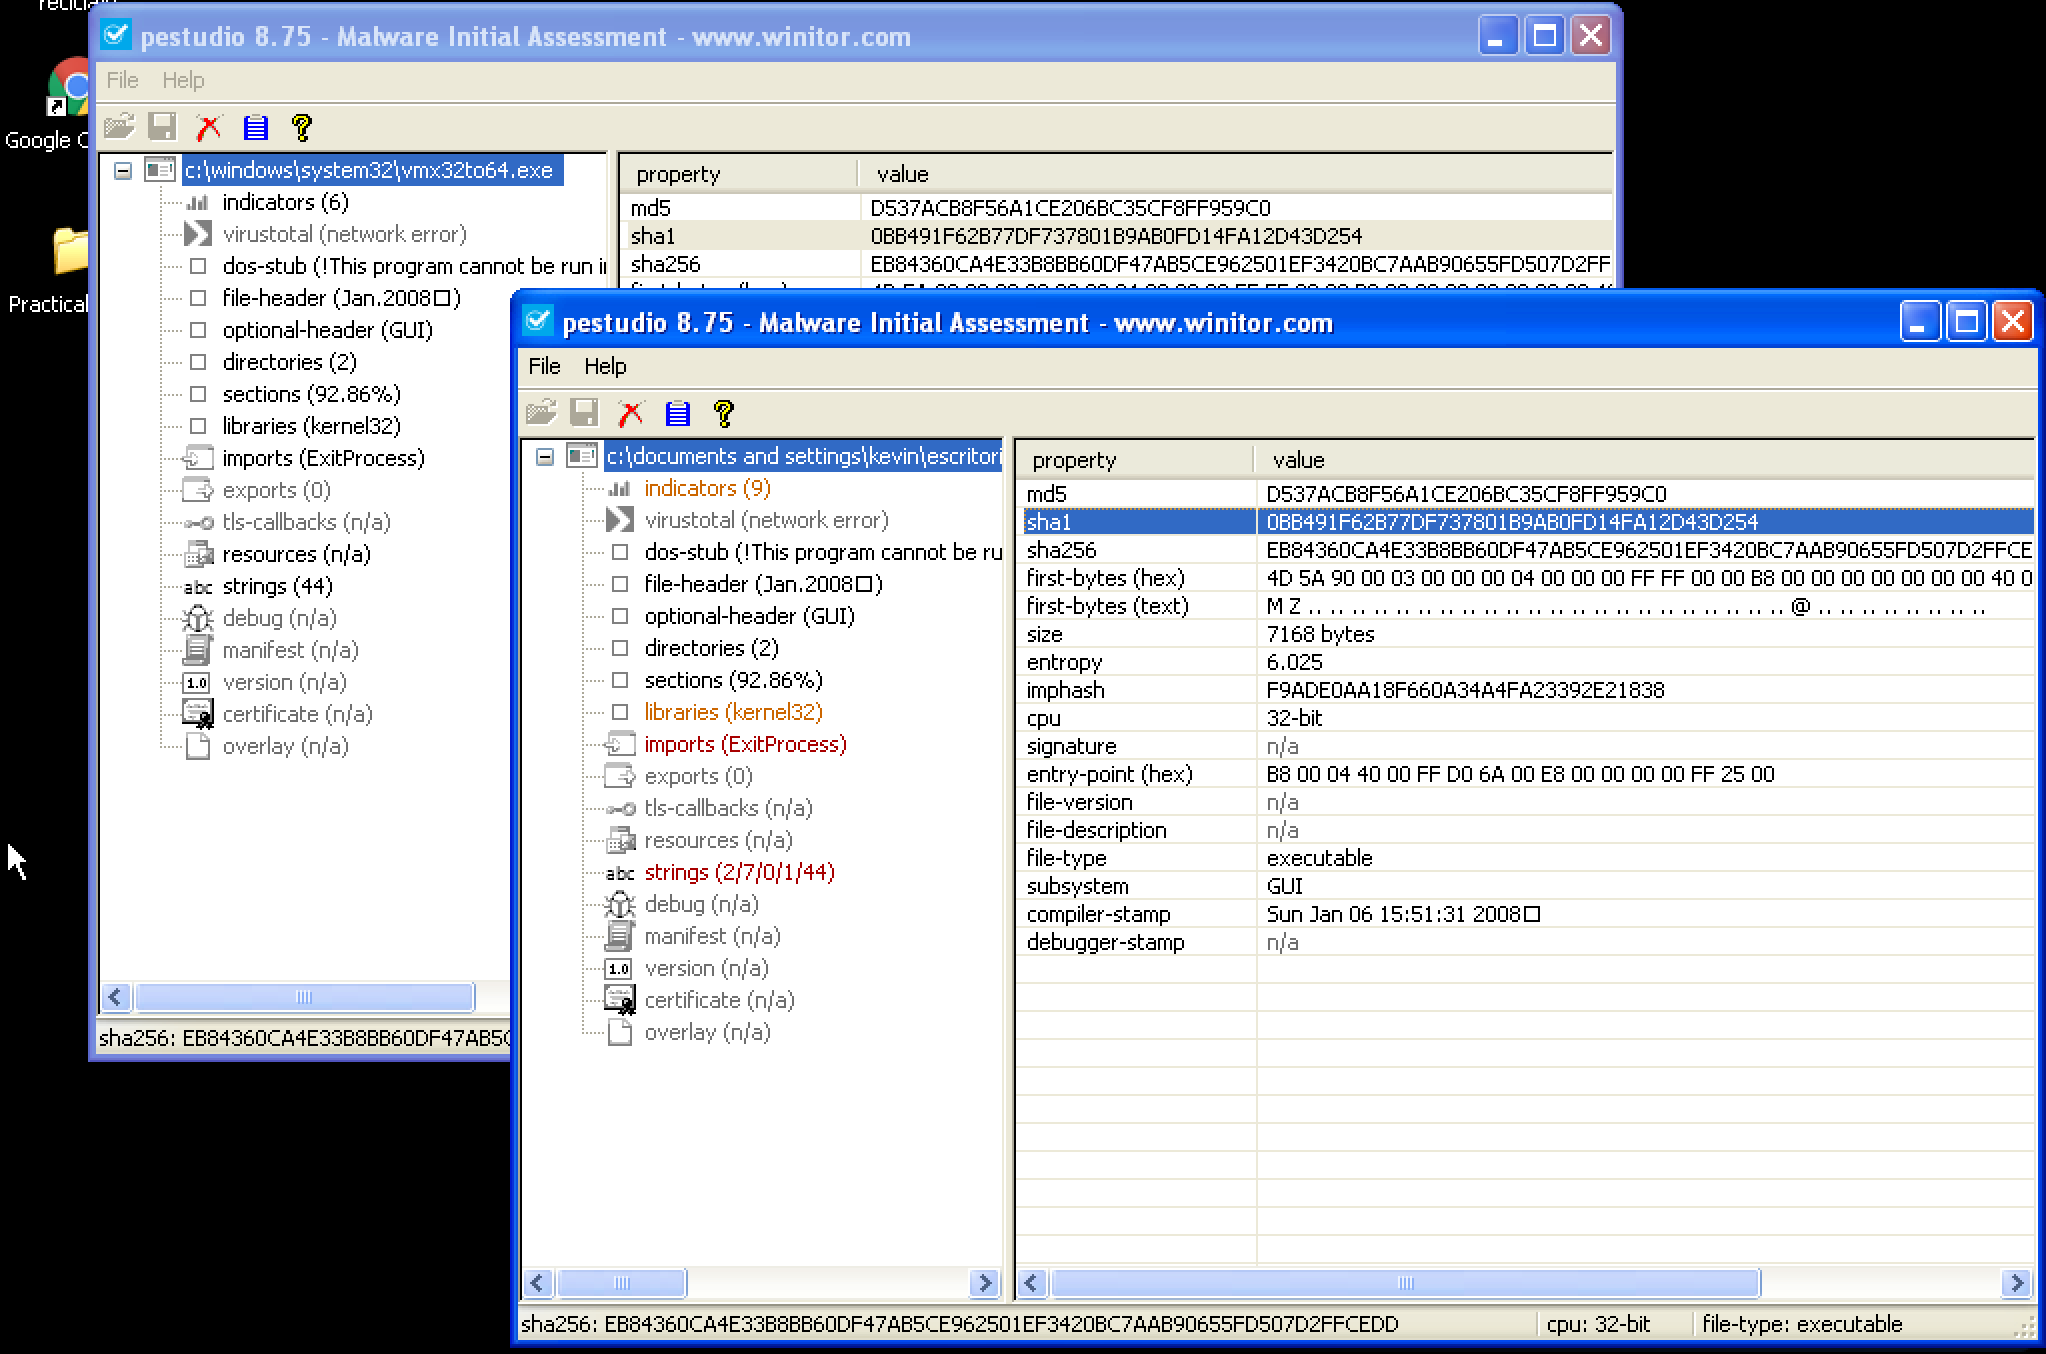
As we can see in the two highlighted events the Malware creates a file: C:\Windows\system32\vmx32to64.exe and maintains persistence by creating a registry entry that executes this file on startup. The file vmx32to64.exe is a copy of Lab03-01.exe.
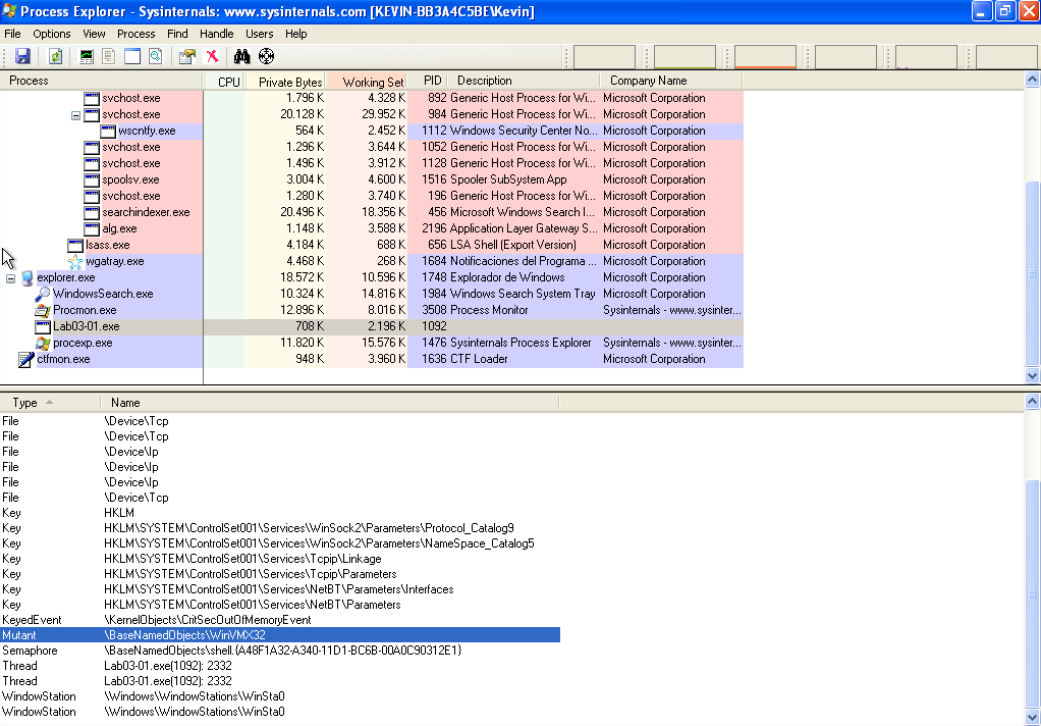
Also, the Malware creates a mutex called WinVMX32.
3) Are there any useful network-based signatures for this malware? If so, what are they?
As we can see the Malware tries to resolve www.practicalmalwareanalysis.com.
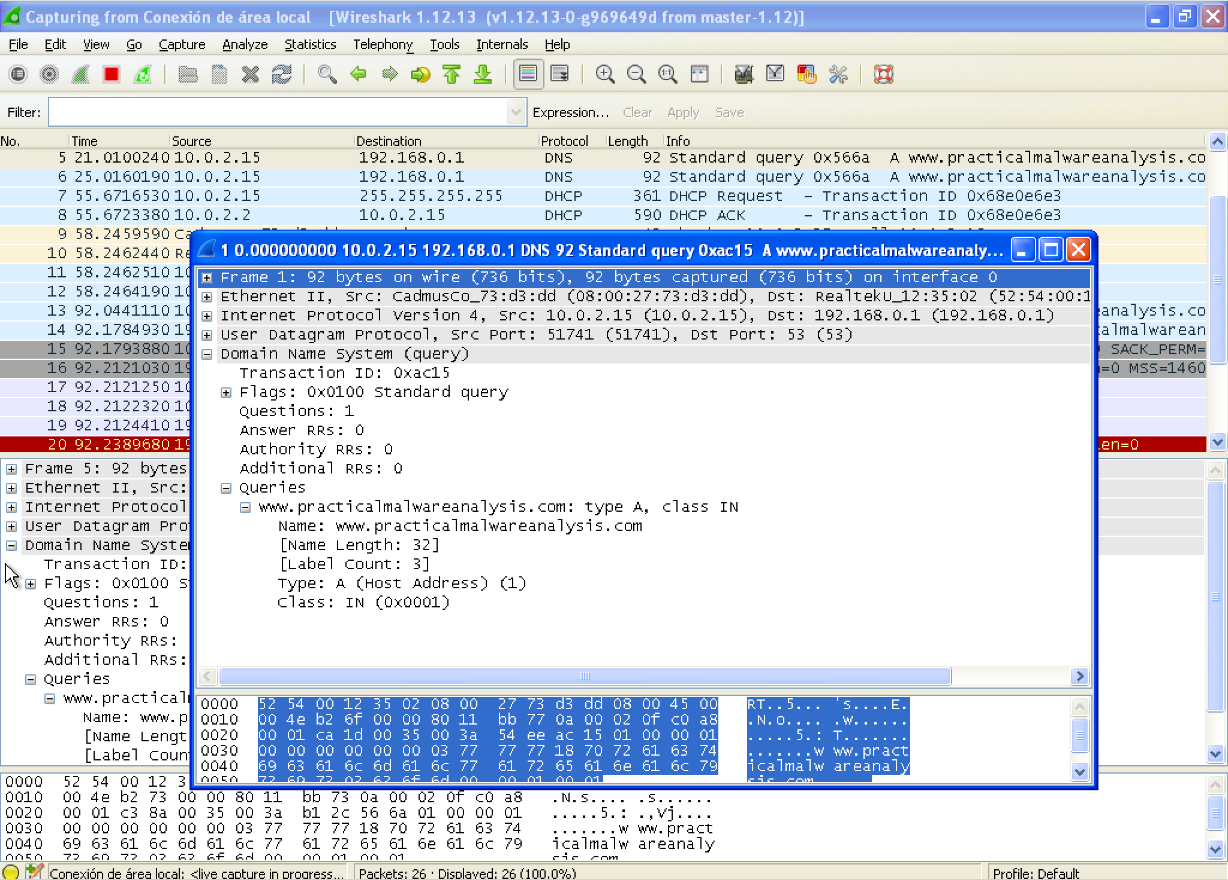
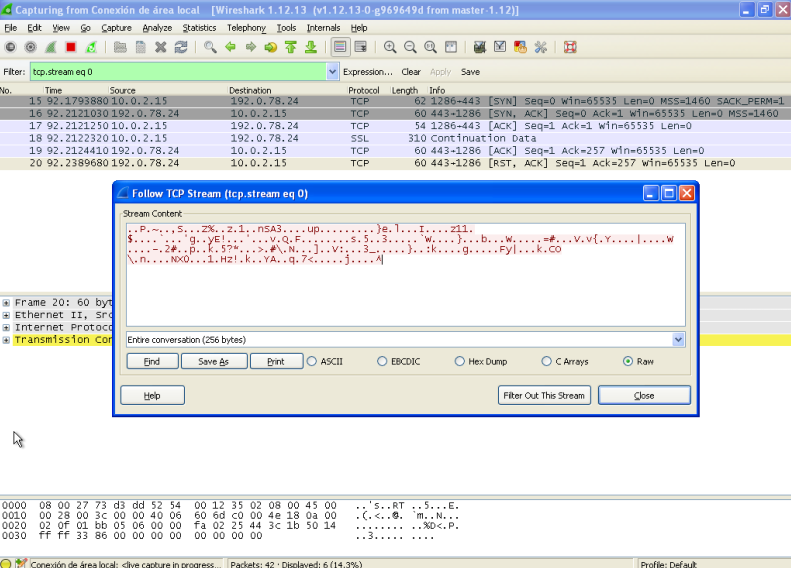
After the malware resolves the name it consistently sends 256 bytes of unreadable data to the server (probably encrypted).