PMA Lab 1-3: Basic Static Analysis
1) Upload the Lab01-03.exe file to http://www.VirusTotal.com/. Does it match any existing antivirus definitions?
Lab 1-3
1) Upload the Lab01-03.exe file to http://www.VirusTotal.com/. Does it match any existing antivirus definitions?
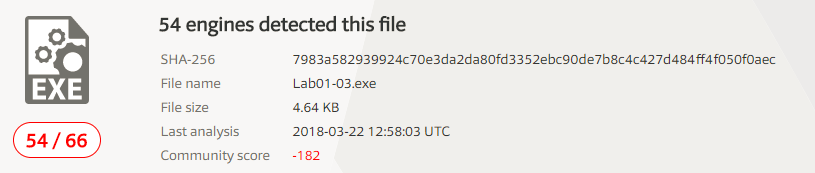
File Lab01-03.exe was first submitted to Virustotal on 2011-07-04 22:00:08 and since then it has as 54/66 detection rate:
File name: Lab01-03.exe
SHA256: 7983a582939924c70e3da2da80fd3352ebc90de7b8c4c427d484ff4f050f0aec
2) Are there any indications that this file is packed or obfuscated? If so, what are these indicators? If the file is packed, unpack it if possible.
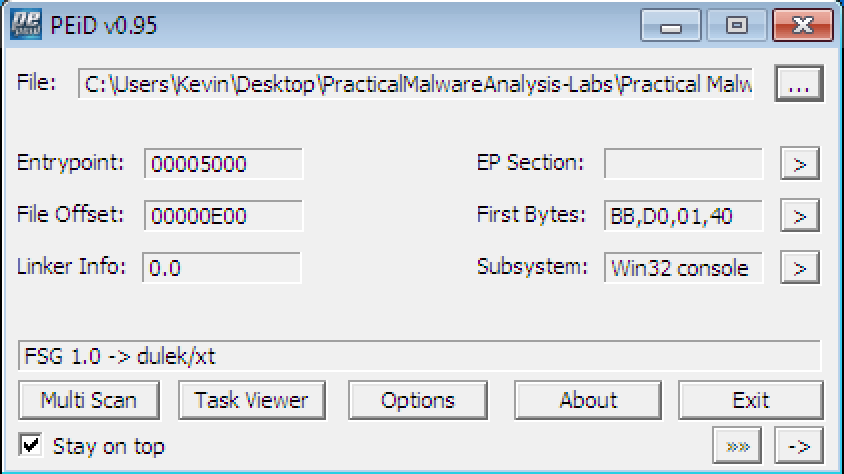
Yes, using PEid we can see that the program is Packed with FSG.
The Malware has a really small amount of Imports: LoadLibraryA and GetProcAddress, usually used when Malwares dynamically resolve the Imports.
Also, we can see that the sections have no names and that the first section has a Virtual Size of 12288 bytes (0x3000) while its Raw Size is 0.
There’s no way of automatically unpack this file, so at this point, it’s not possible to unpack it.
3) Do any imports hint at this program’s functionality? If so, which imports are they and what do they tell you?
The program only has two Imports (LoadLibraryA and GetProcAddress). Having only these two imports we know that the functions that the Malware uses are dynamically resolved and thus, without any further information (without running the Malware) it is not possible to provide any information regarding the program’s functionality other than that.
4) What host- or network-based indicators could be used to identify this malware on infected machines?
It is not possible to provide any host or network-based indicator using Static Analysis without unpacking this file.